


Brute-force & suspicious logins
Failed-logon bursts, RDP/SSH from new sources, off-hours access.
KIROSEC ingests Windows, Linux, macOS, and cloud logs, normalizes them to a canonical event model with searchable structured fields, and runs 329 versioned detection rules and produces technical and executive reports — fully offline.
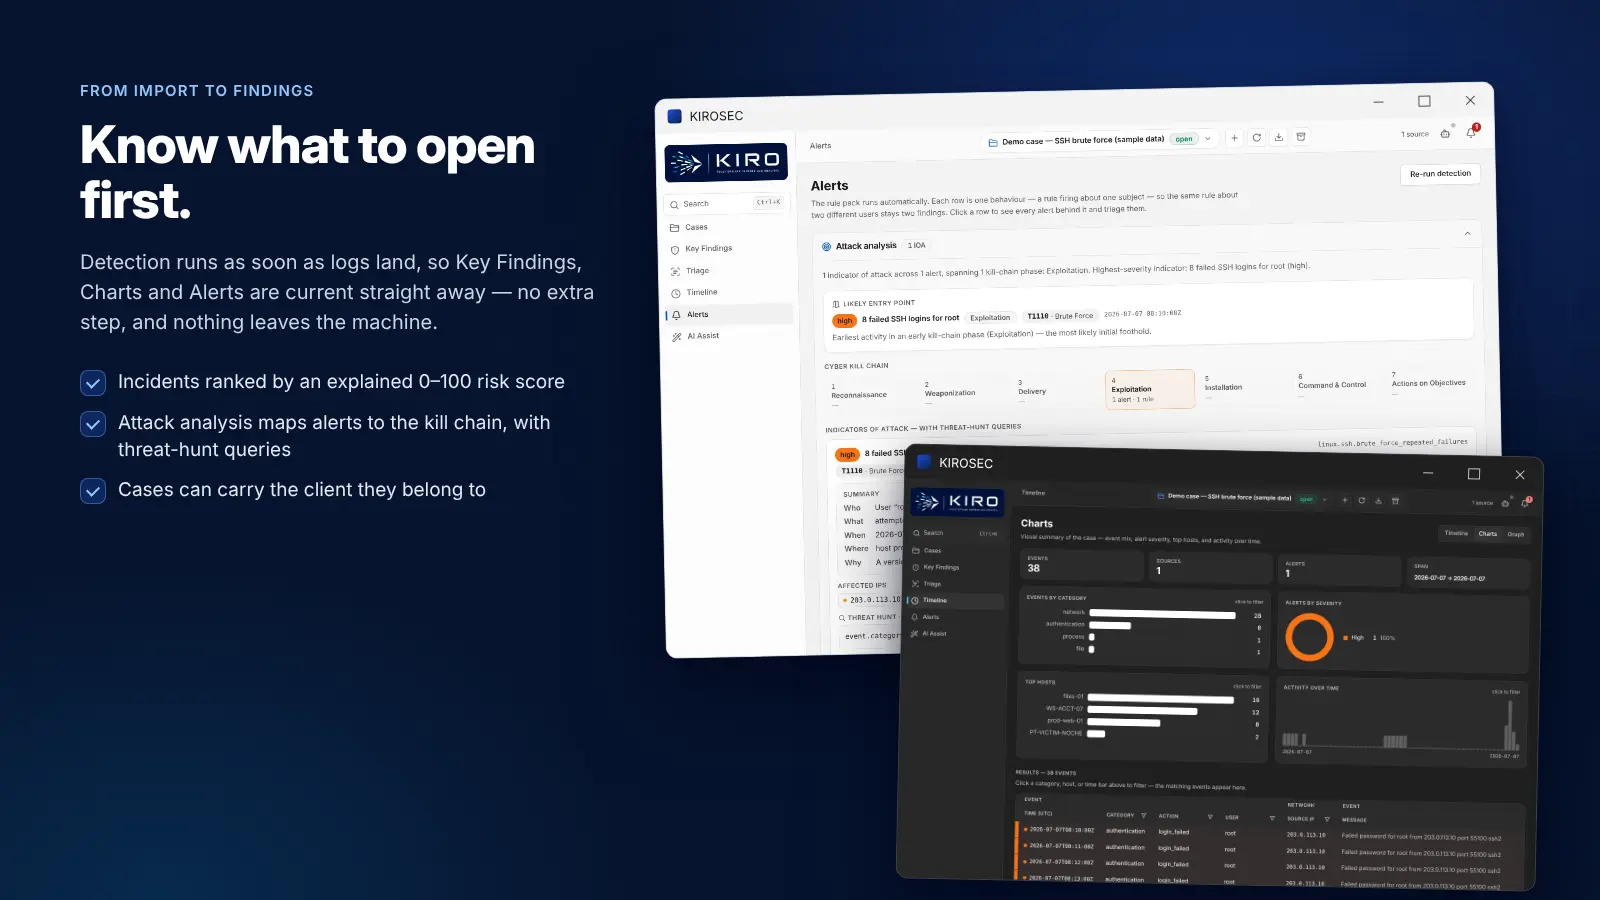
 Screenshot 2 of 5: KIROSEC analysis workspace
$ kiro analyze ./exports --rules stable
imported blue-team-sysmon.csv 36 events
imported windows-security.xml 21 events
imported nginx-access.log 25 events

ran 60 rules over 82 events → 14 alerts
CRITICAL LSASS credential dump (Mimikatz)
CRITICAL shadow copies deleted — ransomware
HIGH known offensive tool — SharpHound.exe
HIGH web exploit succeeded — SQLi (200)
MEDIUM Tor anonymizer launched
KIROSEC hunts for the behaviors attackers rely on to break in, move laterally, and exfiltrate data — even when tools are renamed, logs are missing, or the network is offline.
The real detection engine over a synthetic Microsoft 365 audit sample committed in this repo — no customer data. Drag across the histogram to filter by time; what appears is what the desktop app shows.
Repeated failed cloud sign-ins from one IP against a single user inside a short window — password guessing against the cloud control plane.
6 failures in ~7 min, then 2 successful logons from the same IP — the burst-then-success pattern the engine escalates to a takeover incident.
Drop logs or PowerShell output into Triage — no files, no import. KIROSEC highlights what matters, scores risk, and explains the “why” in plain English.
insight > analyze

HIGH  Brute-force logon from 203.0.113.45
HIGH  PowerShell encoded command launched
MED   New local admin created: svc_backup
LOW   Scheduled task persistence detected

4 findings · 1m 24s
Security analysis you can defend — evidence stays intact, nothing phones home, and our controls are documented against recognized standards.
These are self-assessments we publish in full, not third-party certifications — read the ASVS L2 attestation and the CAIQ v4 self-assessment, open gaps included. We are not listed in the CSA STAR Registry yet, and independent audits (SOC 2, ISO 27001) are on our roadmap.
From raw logs to clear answers in four simple steps.
Built for offline investigations, trusted findings, and analyst speed.
The Offline Edition ships without an HTTP client compiled in — it cannot reach the network, and your security team can verify that themselves before they trust us.

Every finding links to the exact evidence, signed rule, and MITRE technique. Know why it is suspicious.
203.0.113.45MITRET1110Clear summaries, impacted assets, recommended actions, and executive-ready roll-ups.
2 high, 3 medium, 5 low risk findings
From first triage to final report, KIROSEC helps your team move faster with confidence — even in the toughest environments.
Rules are versioned YAML with positive and negative fixtures — data, never executed code, mapped to MITRE ATT&CK. Every finding carries its evidence: source hash, parser version, and the events that triggered it, plus a plain-language 5W story when you need to brief a client.
Drop any raw log line or command into Triage — no case, no import. KIROSEC extracts the fields and indicators (IPs, domains, hashes, CVEs), suggests likely MITRE ATT&CK techniques, explains Entra sign-in codes, and decodes obfuscated PowerShell for you. Nothing is stored.
# paste →
powershell -w hidden -enc SQBFA…

decoded IEX(New-Object Net.WebClient)…
T1059.001 PowerShell
T1105 Ingress Tool Transfer
T1564.003 Hidden Window
Drop in Windows, Linux, macOS, network and cloud logs — EVTX, Sysmon, syslog, M365 and Entra exports, CloudTrail, Okta and more. Zips and rotated logs open directly.
Everything becomes canonical events with honest timestamps and a preserved evidence chain — and nested JSON becomes columns you can actually filter on.
329 versioned rules flag brute force, suspicious execution, persistence, ransomware, exfiltration and cloud identity abuse — then group what belongs together into incidents.
Turn findings into a defensible write-up: evidence-backed, redactable, and readable by someone who was not in the investigation.
We are working with a small group of teams before we open up. Book a demo and we will walk you through the product and where it is heading.
KIROSEC is in closed beta. Book a walkthrough and we will show you a real case end to end — import, detections, and the write-up that comes out.
We use privacy-first, cookieless analytics to understand which pages help — only if you allow it. No third-party trackers, and your IP is never stored for analytics. See our Privacy Policy and Cookie Policy.